
CrossChain Security Best Practices: Bridging Blockchains Safely and Securely

Welcome to Blockchain Trends, your source for understanding the real-world impact of blockchain technology.
Ever wondered how seamlessly data can move between different blockchains without compromising security? Dive into our latest exploration of Crosschain Security Best Practices, a crucial element for the future of decentralized systems. This guide unveils critical strategies and insights to navigate the complex landscape of cross-chain communication and build robust, secure bridges. Uncover the potential and the pitfalls – and discover the best practices for a safer, more interconnected blockchain future.
- Understanding Crosschain Security Risks and Challenges
- Essential Crosschain Security Best Practices: A Comprehensive Guide
- Advanced Crosschain Security Strategies and Techniques
- Crosschain Security Audit Checklist: Ensuring Bridge Integrity
- The Future of Crosschain Security: Innovations and Trends
- Conclusion: Prioritizing Security in the Crosschain Ecosystem
-
Frequently Asked Questions
- How does Crosschain security differ from traditional blockchain security?
- What are some common attack vectors in Crosschain bridges?
- What is the role of Decentralized governance in securing Crosschain bridges?
- What are some Best Practices for implementing secure Crosschain communication?
- How do regulations impact the development and deployment of Crosschain bridges?
- Final Reflection: Navigating the Interconnected Future
- Fortify Your Bridges: Secure Your Cross-Chain Future!
Understanding Crosschain Security Risks and Challenges
The Growing Need for Secure Crosschain Interoperability
The blockchain ecosystem, while revolutionary, is increasingly fragmented. Numerous blockchains exist, each with unique features, consensus mechanisms, and communities. This siloed nature limits the full potential of blockchain technology. Crosschain interoperability, the ability for different blockchains to communicate and transact with each other, is becoming paramount to unlock seamless value transfer, data sharing, and application integration across these diverse networks. Imagine a future where a decentralized application (dApp) on Ethereum can effortlessly access data stored on Filecoin or utilize the fast transaction speeds of Solana – this is the promise of crosschain technology.
However, this interconnected vision introduces significant security challenges. As value and data flow between blockchains, the attack surface expands dramatically. A vulnerability in one chain or in the crosschain bridge connecting them can have cascading effects, potentially compromising assets and operations across multiple networks. The need for robust crosschain security is not merely a technical consideration; it is a fundamental requirement for the sustainable growth and adoption of a truly interoperable blockchain ecosystem. Without prioritizing and implementing strong security measures, the promise of crosschain interoperability risks becoming a liability, vulnerable to exploits and undermining user trust.
Common Vulnerabilities in Crosschain Bridges
Crosschain bridges, acting as conduits for asset and data transfer between blockchains, are inherently complex and represent a significant attack vector. One common vulnerability stems from smart contract flaws within the bridge's architecture. If the smart contracts governing the bridge are poorly coded, contain logic errors, or are susceptible to reentrancy attacks, they can be exploited to drain funds or manipulate transactions. For example, the infamous Poly Network hack in 2021, which resulted in the theft of over $600 million, was attributed to a vulnerability in the bridge's smart contracts that allowed attackers to bypass signature verification.
Another prevalent vulnerability arises from oracle manipulation. Many crosschain bridges rely on oracles to relay information about events occurring on one chain to another. If these oracles are compromised or manipulated, attackers can inject false data, leading to incorrect transaction execution or fund misdirection. Consider a bridge that uses price oracles to determine exchange rates for token swaps.
If an attacker can manipulate the price feed from the oracle, they could potentially execute swaps at artificially favorable rates, draining liquidity from the bridge. Furthermore, centralized or semi-centralized bridges introduce risks associated with single points of failure and custody. If the central entity controlling the bridge is compromised, or its private keys are exposed, the entire bridge and its assets become vulnerable.
Identifying Potential Attack Vectors in Crosschain Transactions
Understanding potential attack vectors is crucial for developing effective crosschain security best practices. Replay attacks are a significant concern, where a valid transaction broadcast on one chain could be replayed on another chain if the bridge doesn't implement sufficient transaction uniqueness checks and chain identification mechanisms. This could lead to duplicate transactions and unauthorized asset duplication or transfers. Routing errors also pose a risk. In complex crosschain networks with multiple bridges and routing paths, misconfigurations or vulnerabilities in routing protocols could lead to transactions being misdirected or intercepted.
Furthermore, denial-of-service (DoS) attacks can target crosschain bridges, aiming to disrupt their operation and prevent legitimate transactions from being processed. By flooding the bridge with spurious requests or exploiting resource limitations, attackers can effectively shut down the bridge, causing significant disruption and potentially creating opportunities for other exploits. Economic exploits, such as those targeting insufficient liquidity in bridge pools or manipulating incentive mechanisms, are also relevant. If a bridge's liquidity pools are shallow, large transactions could cause significant slippage, which can be exploited.
Similarly, flawed incentive structures in bridge protocols could be manipulated to drain funds or disrupt operations. Finally, social engineering attacks targeting bridge operators or users remain a persistent threat. Phishing attacks, key compromise through social engineering, or insider threats can all compromise the security of crosschain bridges and the assets they manage.
Essential Crosschain Security Best Practices: A Comprehensive Guide
Implementing Robust Smart Contract Security for Crosschain Applications
Ensuring the security of smart contracts is paramount for building secure crosschain applications. Given that smart contracts often govern the logic of crosschain bridges and applications, vulnerabilities in these contracts can have far-reaching consequences, affecting multiple blockchains. A proactive and layered approach to smart contract security is essential, encompassing secure coding practices, rigorous testing, formal verification, and independent security audits. This comprehensive strategy minimizes the likelihood of exploitable weaknesses in the core components of crosschain systems.
Prioritizing smart contract security from the outset of development is more cost-effective and efficient than attempting to patch vulnerabilities after deployment. Integrating security considerations into every stage of the software development lifecycle (SDLC), from design and coding to testing and deployment, is crucial. This "security by design" approach helps to prevent common vulnerabilities and ensures that security is not an afterthought.
Furthermore, ongoing monitoring and maintenance of deployed smart contracts are necessary to address newly discovered vulnerabilities and adapt to evolving threat landscapes. Regular security audits and updates should be considered a fundamental part of managing crosschain smart contract security.
Secure Coding Practices for Crosschain Smart Contracts
Secure coding practices form the foundation of robust crosschain smart contract security. Developers must adhere to established secure coding guidelines and best practices specific to smart contract languages like Solidity and Vyper. This includes implementing input validation to prevent injection attacks, carefully managing access control to restrict unauthorized function calls, and avoiding common pitfalls like reentrancy vulnerabilities. Reentrancy attacks, in particular, have been a significant source of exploits in DeFi and crosschain bridges. Developers should utilize well-established patterns like checks-effects-interactions to mitigate reentrancy risks.
Furthermore, thorough error handling and proper logging mechanisms are crucial for debugging and incident response. Smart contracts should be designed to gracefully handle unexpected inputs and errors, preventing them from leading to exploitable states. Detailed logging provides valuable information for diagnosing issues and understanding the behavior of smart contracts, which is essential for security monitoring and incident investigation. Utilizing linters and static analysis tools during development can also help identify potential security vulnerabilities early in the development process. These tools can automatically detect common coding errors and security flaws, improving the overall quality and security of smart contracts.
Formal Verification and Audits for Crosschain Smart Contracts
Formal verification and security audits are critical layers of assurance for crosschain smart contracts. Formal verification employs mathematical techniques to prove the correctness and security properties of smart contracts. By formally verifying smart contracts, developers can gain a high degree of confidence that their code behaves as intended and is free from certain classes of vulnerabilities. While formal verification can be resource-intensive, it provides a rigorous and mathematically sound approach to security assurance, particularly for critical crosschain infrastructure.
Independent security audits conducted by reputable blockchain security firms are also indispensable. Security auditors meticulously review smart contract code, architecture, and deployment processes to identify potential vulnerabilities. These audits often involve both automated and manual analysis, leveraging the expertise of security professionals to uncover subtle or complex security flaws that might be missed by automated tools alone. A comprehensive security audit report provides developers with actionable recommendations for remediating identified vulnerabilities, significantly enhancing the overall security posture of crosschain smart contracts before they are deployed and entrusted with user funds.
Secure Key Management for Crosschain Operations
Secure key management is paramount in crosschain environments, as private keys control access to assets and the ability to initiate transactions across different blockchains. Compromised private keys can lead to catastrophic losses, especially in bridges holding substantial value. A robust key management strategy must encompass secure generation, storage, usage, and rotation of private keys, minimizing the risk of exposure or unauthorized access. This is particularly critical for entities operating crosschain bridges or managing significant crosschain assets.
Traditional key management practices, such as storing private keys on single servers or individual devices, are often inadequate for the high-security demands of crosschain operations. More advanced techniques, such as Multi-Party Computation (MPC) and Hardware Security Modules (HSMs), offer enhanced security and resilience for managing private keys in crosschain contexts. These technologies distribute key management responsibilities and protect keys from physical and digital threats, significantly reducing the risk of single points of failure and key compromise. Choosing the appropriate key management solution depends on the specific security requirements, operational constraints, and risk tolerance of the crosschain application or bridge.
Multi-Party Computation (MPC) for Crosschain Key Management
Multi-Party Computation (MPC) provides a cryptographic approach to distributed key management, ideal for enhancing crosschain security. MPC allows multiple parties to jointly compute a function without revealing their individual inputs. In the context of key management, MPC can be used to distribute the private key across multiple participants, such that no single party holds the entire key. To perform cryptographic operations, such as signing transactions, the participants collaboratively compute a signature using their key shares, without ever reconstructing the complete private key.
This distributed key management approach significantly reduces the risk of key compromise, as an attacker would need to compromise multiple parties to gain control of the private key. MPC is particularly valuable for crosschain bridges and applications that require decentralized control and enhanced security against insider threats or single points of failure. Various MPC protocols exist, each with different performance characteristics and security assumptions. Selecting an appropriate MPC protocol and carefully implementing it are crucial for realizing its security benefits in crosschain key management.
Hardware Security Modules (HSMs) for Protecting Crosschain Keys
Hardware Security Modules (HSMs) offer a robust hardware-based solution for securing private keys used in crosschain operations. HSMs are tamper-resistant hardware devices designed to securely generate, store, and manage cryptographic keys. They provide a physically isolated and hardened environment for sensitive cryptographic operations, protecting private keys from software vulnerabilities and physical attacks. HSMs are often certified to meet stringent security standards, such as FIPS 140-2, providing a high level of assurance for key protection.
In crosschain contexts, HSMs can be used to secure the private keys of bridge operators, validators, or other critical entities involved in crosschain transactions. By storing private keys within HSMs, organizations can significantly reduce the risk of key theft or unauthorized access, even in the event of system compromise.
HSMs can be integrated with crosschain applications and bridges to perform cryptographic operations securely, ensuring that private keys never leave the protected HSM environment. While HSMs can be more expensive and complex to implement than software-based key management solutions, they offer a superior level of security for high-value crosschain assets and critical infrastructure.
Strengthening Consensus Mechanisms in Crosschain Protocols
Consensus mechanisms are the backbone of blockchain security, ensuring agreement and immutability of the ledger. In crosschain protocols, robust consensus mechanisms are essential not only for individual chains but also for the crosschain interactions themselves. Weaknesses in consensus mechanisms can be exploited to compromise the integrity of crosschain transactions, leading to double-spending, fraudulent transfers, or network disruptions. Therefore, strengthening consensus mechanisms is a critical aspect of crosschain security best practices.
Crosschain protocols often involve coordinating consensus across multiple independent blockchains. This introduces new challenges compared to single-chain consensus. For example, ensuring atomic crosschain transactions, where either all parts of the transaction succeed or all fail, requires careful coordination of consensus mechanisms across participating chains. Furthermore, the latency and reliability of communication between chains can impact the overall security and performance of crosschain consensus. Designing and implementing robust consensus mechanisms that can effectively handle these challenges is crucial for building secure and reliable crosschain systems.
Fault Tolerance and Byzantine Fault Tolerance (BFT) in Crosschain Systems
Fault tolerance and Byzantine Fault Tolerance (BFT) are crucial properties for consensus mechanisms in crosschain systems. Fault tolerance refers to the ability of a system to continue operating correctly even when some of its components fail.
In the context of crosschain consensus, this means that the system should be able to withstand failures of individual nodes or even entire blockchains without compromising the security or integrity of crosschain transactions. Byzantine Fault Tolerance (BFT) is a more specific and stronger form of fault tolerance that addresses scenarios where nodes can not only fail but also act maliciously or deceptively, sending incorrect or conflicting information.
BFT consensus mechanisms are particularly relevant for crosschain systems, where participants may have different levels of trust and may not fully trust each other. BFT algorithms, such as Practical Byzantine Fault Tolerance (pBFT) or Tendermint, are designed to tolerate a certain number of Byzantine faults, ensuring that the system can still reach consensus even in the presence of malicious actors.
Implementing BFT consensus in crosschain protocols enhances their resilience against attacks and ensures the reliability of crosschain transactions even in adversarial environments. Choosing and correctly implementing a suitable BFT consensus algorithm is a key aspect of designing secure crosschain systems.
Implementing Watchtowers and Relayers for Monitoring Crosschain Activity
Watchtowers and relayers play vital roles in monitoring and securing crosschain activity. Watchtowers are independent entities that monitor blockchain networks for specific events, such as crosschain transactions or suspicious activities. They act as sentinels, continuously observing the state of the blockchain and alerting relevant parties to potential security issues or anomalies. Relayers, on the other hand, are responsible for relaying messages or transactions between different blockchains, facilitating crosschain communication.
In the context of security, both watchtowers and relayers can be leveraged to enhance crosschain security monitoring and incident response. Watchtowers can detect unusual patterns or suspicious transactions on crosschain bridges, providing early warnings of potential attacks. They can also monitor the behavior of relayers, ensuring they are acting honestly and according to protocol.
Relayers themselves can be designed with security features, such as fraud proofs or challenge mechanisms, to prevent malicious relayers from manipulating crosschain transactions. Implementing a network of robust watchtowers and secure relayers is a valuable strategy for enhancing the overall security and transparency of crosschain systems, allowing for proactive detection and mitigation of security threats.
Advanced Crosschain Security Strategies and Techniques
Utilizing Zero-Knowledge Proofs (ZKPs) for Private Crosschain Transfers
Zero-Knowledge Proofs (ZKPs) are a powerful cryptographic tool that can significantly enhance privacy and security in crosschain transfers. ZKPs allow one party (the prover) to prove to another party (the verifier) that a statement is true, without revealing any information beyond the validity of the statement itself. In the context of crosschain transfers, ZKPs can be used to prove that a transaction is valid and authorized without revealing sensitive details about the transaction, such as the sender, receiver, or the amount being transferred.
This privacy-preserving property of ZKPs is particularly valuable in crosschain scenarios where users may want to maintain confidentiality of their transactions across different blockchains. For example, ZKPs can enable private crosschain swaps, where users can exchange tokens between different chains without revealing the details of the swap to public observers. Furthermore, ZKPs can enhance security by reducing the amount of information that needs to be exposed on-chain, minimizing the potential attack surface. Implementing ZKP-based crosschain transfer mechanisms requires careful design and integration, but the privacy and security benefits they offer are substantial.
Implementing Threshold Signatures for Enhanced Crosschain Security
Threshold signatures offer another advanced cryptographic technique to bolster crosschain security. Threshold signatures are a type of digital signature scheme where multiple parties collectively generate a signature, but no single party can create a valid signature on their own. A threshold signature scheme requires a minimum number of participants (the threshold) to cooperate in order to produce a valid signature. This distributed signature generation process enhances security by eliminating single points of failure and mitigating the risk of key compromise.
In crosschain applications, threshold signatures can be used to secure multi-signature wallets, bridge operators, and other critical components that require distributed control and enhanced security. For example, a crosschain bridge could use a threshold signature scheme to require multiple bridge operators to collectively authorize crosschain transactions, preventing any single operator from unilaterally controlling the bridge's funds. Threshold signatures increase the resilience of crosschain systems against attacks, as compromising a single participant is insufficient to compromise the security of the system.
Various threshold signature schemes exist, with different performance and security trade-offs. Choosing and implementing an appropriate threshold signature scheme depends on the specific security and operational requirements of the crosschain application.
Exploring Optimistic Rollups and Validium for Scalable and Secure Crosschain Solutions
Optimistic Rollups and Validium are layer-2 scaling solutions that can also contribute to more scalable and secure crosschain interactions. These technologies process transactions off-chain and periodically submit compressed transaction data and state roots to the main chain (layer-1). Optimistic Rollups assume transactions are valid by default and use fraud proofs to challenge invalid transactions. Validium, on the other hand, uses validity proofs, such as ZK-SNARKs or ZK-STARKs, to cryptographically prove the validity of off-chain transactions before submitting them to the main chain.
In crosschain contexts, Optimistic Rollups and Validium can be used to create more efficient and secure bridges. By processing crosschain transactions off-chain and leveraging fraud or validity proofs on the main chain, these technologies can significantly reduce transaction costs and increase throughput compared to traditional crosschain bridges that rely on on-chain transaction processing for every crosschain interaction.
Furthermore, the security of Optimistic Rollups and Validium is anchored to the security of the main chain, providing a strong security foundation for crosschain operations. While still relatively nascent, Optimistic Rollups and Validium hold significant promise for building scalable and secure crosschain solutions.
Crosschain Security Audit Checklist: Ensuring Bridge Integrity
Key Areas to Evaluate During a Crosschain Security Audit
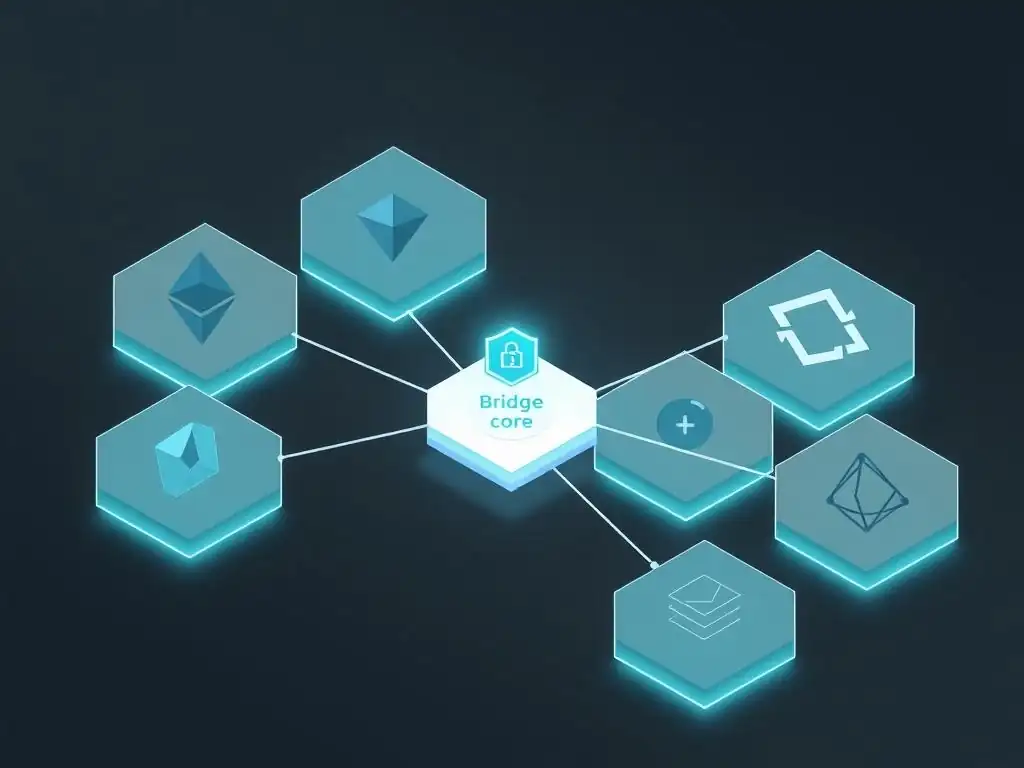
A comprehensive crosschain security audit is crucial to ensure the integrity and robustness of crosschain bridges and applications. The audit should cover various key areas, including smart contract security, cryptographic implementations, consensus mechanisms, key management practices, and operational security. In smart contract security, auditors should meticulously review the code for vulnerabilities such as reentrancy, integer overflows, and access control issues, paying particular attention to the logic governing crosschain interactions and asset transfers. Cryptographic implementations should be assessed for the use of secure and well-vetted cryptographic algorithms and libraries, ensuring proper key generation, storage, and usage.
The audit should also evaluate the consensus mechanisms employed by the crosschain protocol and participating blockchains, examining their fault tolerance, BFT properties, and resistance to various attack vectors. Key management practices should be thoroughly reviewed, assessing the security of key generation, storage, access control, and rotation procedures. Operational security considerations, such as incident response plans, monitoring systems, and access control policies for bridge operators, should also be examined. A holistic audit approach that covers all these key areas is essential to identify and address potential security weaknesses in crosschain systems.
Tools and Resources for Conducting Crosschain Security Audits
Several tools and resources are available to assist in conducting thorough crosschain security audits. Static analysis tools, such as Slither, Mythril, and Securify, can automatically detect common vulnerabilities in smart contract code, helping auditors to identify potential security flaws efficiently.
Fuzzing tools can be used to test the robustness of smart contracts by feeding them with a wide range of inputs, uncovering unexpected behavior or vulnerabilities that might not be apparent through static analysis alone. Formal verification tools, while more complex to use, can provide mathematical proofs of the correctness and security properties of smart contracts, offering a high level of assurance.
Beyond automated tools, various online resources and communities can provide valuable information and support for crosschain security audits. Blockchain security firms often publish blog posts, research papers, and security advisories that share insights into common vulnerabilities and best practices. Online forums and communities dedicated to blockchain security can be valuable for exchanging knowledge, asking questions, and staying up-to-date on the latest security threats and mitigation techniques. Leveraging a combination of automated tools, expert knowledge, and community resources is crucial for conducting effective and comprehensive crosschain security audits.
Common Audit Findings and Remediation Strategies
Crosschain security audits often reveal recurring patterns of vulnerabilities and common findings. Reentrancy vulnerabilities in smart contracts, particularly in bridges that handle asset transfers, are a frequent finding. Insecure key management practices, such as storing private keys in plaintext or relying on single points of failure, are also common. Oracle manipulation vulnerabilities, arising from reliance on untrusted oracles, are another recurring issue, especially in bridges that depend on external data feeds for transaction execution. Insufficient input validation in smart contracts and crosschain communication protocols can also lead to various injection attacks.
Remediation strategies for these common findings vary depending on the specific vulnerability. For reentrancy vulnerabilities, implementing checks-effects-interactions patterns and using reentrancy guards are effective mitigation techniques. For insecure key management, adopting MPC or HSM-based key management solutions is recommended.
To address oracle manipulation risks, using decentralized and reputable oracle networks, implementing data validation and aggregation techniques, and employing redundancy measures can enhance security. For input validation issues, rigorously validating all inputs and sanitizing data before processing it in smart contracts and crosschain protocols is crucial. Addressing these common audit findings proactively can significantly improve the security posture of crosschain systems.
The Future of Crosschain Security: Innovations and Trends
Advancements in Crosschain Communication Protocols
The future of crosschain security is intertwined with advancements in crosschain communication protocols. Current crosschain bridges often rely on centralized or federated models, which introduce security risks and limitations. Innovations are focusing on developing more decentralized and secure crosschain communication protocols that minimize trust assumptions and enhance security. LayerZero, for instance, utilizes an ultra-light node on-chain and off-chain oracles to achieve secure and efficient message passing between blockchains. IBC (Inter-Blockchain Communication protocol) from Cosmos offers a standardized protocol for interoperability between sovereign blockchains, emphasizing security and sovereignty.
Research and development are also exploring novel cryptographic techniques for secure crosschain communication, such as zero-knowledge succinct non-interactive arguments of knowledge (zk-SNARKs) and zero-knowledge succinct transparent arguments of knowledge (zk-STARKs) to enable verifiable and private crosschain message passing. Furthermore, advancements in light client technology are making it more efficient and secure to verify the state of remote blockchains, enabling trust-minimized crosschain communication without relying on full nodes. These advancements in crosschain communication protocols are paving the way for a more secure and interoperable blockchain ecosystem.
The Role of AI and Machine Learning in Detecting Crosschain Threats
Artificial intelligence (AI) and machine learning (ML) are emerging as valuable tools for enhancing crosschain security, particularly in threat detection and anomaly analysis. AI/ML algorithms can be trained to analyze vast amounts of crosschain transaction data, network traffic, and security logs to identify patterns and anomalies that may indicate malicious activity or security vulnerabilities. For example, ML models can be trained to detect unusual transaction patterns, such as large or frequent crosschain transfers to suspicious addresses, which could signal potential hacks or exploits.
AI-powered security systems can also proactively identify potential vulnerabilities in crosschain bridges and protocols by analyzing smart contract code, network configurations, and security policies. By continuously monitoring crosschain activity and proactively identifying threats, AI/ML can significantly enhance the security posture of crosschain systems and enable faster incident response. However, it's important to note that AI/ML is not a silver bullet for security.
It should be used as a complementary tool alongside other security measures, such as robust cryptographic protocols, secure coding practices, and regular security audits. The effectiveness of AI/ML-based security systems depends heavily on the quality of training data and the sophistication of the algorithms used.
Novel Crosschain Security Technologies and Solutions
The field of crosschain security is rapidly evolving, with continuous development of novel technologies and solutions to address emerging threats and challenges. Homomorphic encryption, which allows computations to be performed on encrypted data without decrypting it first, is being explored for privacy-preserving crosschain computations and data sharing. Secure enclaves, hardware-based secure execution environments, can be used to isolate and protect sensitive code and data in crosschain systems, enhancing security against software-based attacks. Multi-signature schemes with advanced features like threshold signatures and aggregate signatures are becoming increasingly prevalent for securing multi-party crosschain operations.
Furthermore, research into formal verification techniques is advancing, making it more practical and scalable to formally verify the security properties of complex crosschain protocols and smart contracts. Decentralized identity (DID) and verifiable credentials (VC) are being explored to enable secure and privacy-preserving identity management across different blockchains, facilitating secure crosschain interactions. These novel crosschain security technologies and solutions are continuously pushing the boundaries of what is possible in building more secure and interoperable blockchain systems, promising a future where crosschain interactions are both seamless and robustly protected.
Conclusion: Prioritizing Security in the Crosschain Ecosystem
Building a More Secure and Interoperable Blockchain Future
The journey towards a truly interoperable blockchain future hinges on prioritizing security at every layer of crosschain technology. As the blockchain ecosystem matures and crosschain interactions become more prevalent, the potential consequences of security breaches in crosschain bridges and applications will only amplify. Building a secure and interoperable blockchain future requires a collective effort from developers, researchers, security experts, and the broader blockchain community. This collaborative approach should focus on developing and implementing robust crosschain security best practices, fostering a culture of security awareness, and continuously innovating to address emerging threats and vulnerabilities.
Adopting a "security-first" mindset in crosschain development is paramount. This means integrating security considerations into every stage of the development lifecycle, from design and architecture to coding, testing, and deployment. It also involves ongoing monitoring, maintenance, and incident response planning to ensure that crosschain systems remain secure and resilient over time. By collectively prioritizing security, the blockchain community can unlock the full potential of crosschain interoperability, creating a more connected, efficient, and secure blockchain ecosystem for the benefit of all users.
The Importance of Continuous Monitoring and Improvement of Crosschain Security Measures
Crosschain security is not a static destination but an ongoing process that requires continuous monitoring and improvement. The threat landscape is constantly evolving, with new vulnerabilities and attack vectors emerging regularly. Therefore, crosschain security measures must be continuously evaluated, updated, and improved to stay ahead of potential threats. Regular security audits, penetration testing, and vulnerability assessments are essential to identify and address weaknesses in crosschain systems proactively. Monitoring systems should be implemented to detect anomalies and suspicious activities in real-time, enabling rapid incident response.
Furthermore, staying informed about the latest security research, best practices, and emerging threats is crucial for maintaining a strong crosschain security posture. Participating in security communities, attending security conferences, and continuously learning about new security technologies and techniques are essential for security professionals and developers working in the crosschain space. Embracing a culture of continuous improvement and proactively adapting to the evolving security landscape are vital for ensuring the long-term security and sustainability of the crosschain ecosystem.
Frequently Asked Questions
How does Crosschain security differ from traditional blockchain security?
Traditional blockchain security focuses on a single chain, while Crosschain security addresses the vulnerabilities that arise when assets and data move between different blockchains. This requires new mechanisms for consensus and trust.
What are some common attack vectors in Crosschain bridges?
Common attack vectors include smart contract vulnerabilities, validator collusion, and key management compromises. These can lead to significant asset losses on both the source and destination chains.
What is the role of Decentralized governance in securing Crosschain bridges?
Decentralized governance can improve security by distributing control and reducing the risk of centralized failure points. This involves community participation in decision-making related to bridge parameters and upgrades.
What are some Best Practices for implementing secure Crosschain communication?
Best Practices include using audited smart contracts, implementing multi-signature schemes, and employing formal verification methods. Regular security audits are also crucial.
How do regulations impact the development and deployment of Crosschain bridges?
Regulations are evolving, but often focus on KYC/AML compliance and consumer protection. Crosschain bridge developers must stay informed about regulatory requirements to ensure legal compliance and user safety.
The exploration of cross-chain security best practices is not merely an academic exercise; it's a critical imperative for the future of decentralized finance. As blockchains increasingly interconnect, the vulnerabilities inherent in these bridges become amplified, posing a systemic risk to the entire ecosystem. Understanding and implementing robust security measures is no longer optional, but essential for fostering trust and enabling the widespread adoption of cross-chain technology.
The impact of secure cross-chain communication extends far beyond the technical realm, shaping the very fabric of our digital interactions. The ability to seamlessly and securely transfer value and data across different blockchains unlocks unprecedented opportunities for innovation and collaboration. Security is not a product, but a process.
This quote underscores the ongoing nature of security in the cross-chain space, demanding constant vigilance and adaptation to emerging threats.
As you navigate the evolving landscape of blockchain technology, remember that security is a shared responsibility. Take the insights gleaned from this guide and apply them to your own projects, fostering a culture of security awareness and collaboration. By prioritizing cross-chain security, we can collectively build a more resilient, trustworthy, and interconnected future for all.
Fortify Your Bridges: Secure Your Cross-Chain Future!
Thank you for exploring these essential cross-chain security best practices with us. You've gained valuable insights into safeguarding your blockchain interactions. Now, it's time to put that knowledge into action!
Consider taking these immediate steps:
- Prioritize security audits of your cross-chain applications. Conducting proactive vulnerability assessments is your best defense.
- Research the security models of the blockchains you're connecting. Understanding their nuances can help you reduce potential risks.
- Share this article with your network to help others enhance their cross-chain security and contribute to a safer, more resilient blockchain ecosystem.
What security measure will you implement first to strengthen your cross-chain bridges? Share your plans in the comments below!
Leave a Reply